
Commented FALHA? Here is the setup guide for Cloudflare's Security Audit skill, to review your own application's source code. You don't need to put your site online.
A skill is a set of instructions and scripts that teaches your coding agent a task. This one maps the app, then assigns independent agents to look for problems in login, customer data and databases, APIs and webhooks, deployment, dependencies, and, if applicable, prompt injection and data leaks in AI features. A fresh agent tries to disprove each candidate. Think of a security team checking its own work, not a guarantee of safety.
Before you start
Have a terminal, access to code you own, and a coding agent with tools and parallel subagents. Claude Code is one option; Codex and Cursor can also receive skills through the Skills CLI, provided your session supports parallel subagents. Check your agent's permissions and costs. Back up or commit your work, keep secrets out of the context and do not expose real customer data.
Install Node.js and open your project
Install the LTS release for your OS from nodejs.org/download. Reopen your terminal and check:
node --version && npm --versionMove into your own project's folder (replace the path):
cd /path/to/your-projectInstall the skill and request an audit
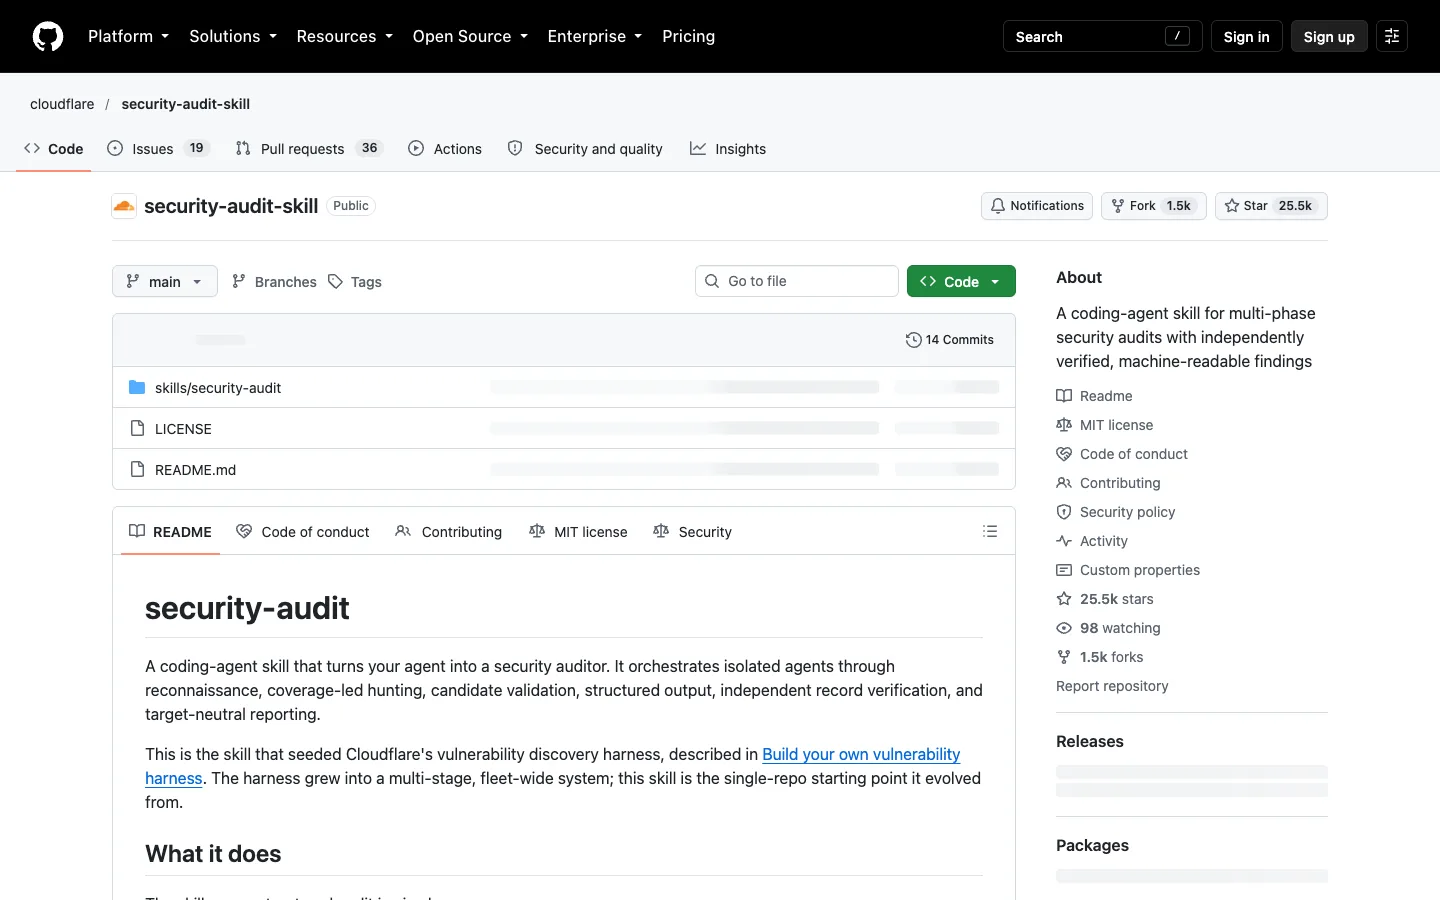
Run Cloudflare's official command in the project folder. npx may ask to install the Skills CLI; read that prompt first. In the menu, choose your coding agent and project-level installation. Restart the agent if it doesn't see the skill.
npx skills add https://github.com/cloudflare/security-audit-skill --skill security-auditOpen Claude Code in the project:
claudeIf Claude Code isn't installed, follow its official setup and sign in yourself. In Codex or Cursor, open the same folder and check that the skill was discovered. Paste this example request into your agent:
Security audit this codebase with the security-audit skill. Write the report in English. Review only this code; do not test live websites, external services or third-party data. Do not change my application code. Execute target code only in an isolated, network-disabled sandbox; otherwise mark the lead needs_validation. Tell me the exact report location.The skill writes architecture.md and coverage-ledger.json during reconnaissance, uses independent agents for hunting and disproof, validates findings.json, and produces REPORT.md, FINDINGS-DETAIL.md, and NEEDS-VALIDATION.md. By default, unspecified output goes under ~/security-audit-skill/, not necessarily inside your repository. Ask the agent for the exact location. This example prompt has not been tested inside Claude Code.
Read the report, fix and run again
Open REPORT.md at the reported location. For each finding check severity, the file and source trace, attack path, evidence, proposed fix, and regression test. See FINDINGS-DETAIL.md for context and NEEDS-VALIDATION.md for unresolved leads.
confirmed: backed by evidence and independent checking; still review it yourself.needs_validation: an exact fact remains unresolved. No confirmed severity; not a proven bug.rejected: the candidate was disproved; not an outstanding fix.
The skill does not automatically edit your application. Review and apply the fix yourself, write or run a regression test that fails before and passes after, and rerun the audit. Cloudflare says one run found roughly half the vulnerabilities found across repeated runs in its tests. More coverage is useful, but no clean report proves your app has no flaws.
Quick FAQ
Is it free? The skill is free under the MIT license. It runs on your agent; model calls, tokens or a subscription may cost money. Check your provider's current pricing as of 7 October 2026. No fixed per-audit price exists.
Is it safe on my code? Your agent can access the files and permissions you give it. Review the skill before installing, exclude keys and customer data, limit permissions and sandbox any execution of target code.
Does it change my code? The audit describes issues and fixes; it does not automatically patch your application. The sample prompt explicitly forbids changes. Check your working tree afterward.
Can I test someone else's site? No. The skill forbids testing live sites, external services or third-party data. Work on code you own or are explicitly authorized to audit, within that scope.
Can I request Portuguese? Yes, ask your agent for a Portuguese report. The skill instructions are in English and output quality depends on your agent.
Cloudflare released this skill in June 2026 as a starting point for its larger harness. The 7,245 actionable findings across 145 repositories in Cloudflare's blog belong to the entire internal system, not this skill by itself. On 7 October 2026, W3Techs estimated Cloudflare on 25.1% of all sites, more than one in five. Evidence and limitations: sources document.
Comments
Have a question or something to add? Join the conversation.
No account needed. Select Sign in and choose a name to comment.
Loading the conversation…
Comment privacyCommenting guidelines